OPC-UA
OPC-UA (OLE for Process Control - Unified Architecture, IEC 62541) is a standard communication protocol for industrial automation. Almost all SCADA / middleware products, such as Kepware, Matrikon, Prosys, and Ignition, provide OPC-UA server functionality.
Since most PLCs do not have native OPC-UA server capabilities, PLC values are typically exposed as OPC-UA via gateway software such as Kepware, and the gateway connects to that OPC-UA server to retrieve the values.
The OPC-UA client in this gateway is based on the Eclipse Milo 1.1.8 SDK.
- Transport: opc.tcp:// (UA Binary encoding)
- Security Mode:
None·Sign·SignAndEncrypt· Automatic — See Secure Connection below - Security Policy: Automatic ·
Aes256_Sha256_RsaPss·Basic256Sha256·Aes128_Sha256_RsaOaep(Legacy policiesBasic256·Basic128Rsa15must be explicitly allowed) - User Authentication: Anonymous or Username + Password
- Read / Write: Both supported. Reading uses
timecyclecycle polling; UA Subscription (MonitoredItem) is not used.
When connecting to the OPC UA servers of DCS or robot controllers, please refer to Connecting DCS · Connecting Robots.
Registration Form Input Values
Below the IP and Port, the OPC UA Protocol Options group contains four fields: Server Name, User, Password, and Discovery. Channel encryption is determined in the Security (Channel Encryption) group below — see Secure Connection.
| Input Field | Description | Example |
|---|---|---|
| IP Address | IP of the OPC-UA server PC | 192.168.0.40 |
| Port | OPC-UA server port | 49320 (Kepware default) / 4840 (Standard) |
| Server Name (servername) | Path portion of the endpoint URI | Leave blank, or OPCUAServer · iotgateway etc. |
| User (username) | User ID registered on the OPC-UA server. Leave blank for anonymous | kopens (Varies by server) |
| Password (password) | Password for the user | *** |
| Discovery (discovery) | If true, browses the entire node tree upon connection | false (Recommended) |
If both User and Password are entered, the connection uses a username token; if either is blank, it connects as Anonymous. For anonymous connections, the server must allow anonymous access. Since accounts are sent over a plaintext channel if the security mode is None, SignAndEncrypt is recommended when using accounts.
How Endpoints Are Determined
- The gateway creates
opc.tcp://<IP>:<port>/<servername>from the input values and requests the endpoint list from the server. - It selects an endpoint from the list that matches the security mode and security policy.
- Security Mode None: Among None endpoints, one that advertises the required user token (anonymous or username) is prioritized; otherwise, the first None endpoint is used.
- Sign · SignAndEncrypt · Automatic: Among endpoints satisfying both the selected mode/policy and the user token, the strongest policy is chosen. If no match is found, it fails to connect without falling back to None (
OPCUA_NO_MATCHING_ENDPOINT).
- The host of the selected endpoint URL is replaced with the entered IP for connection (port and path use the values advertised by the server). DNS or hosts configuration is not required even if the server advertises its own hostname.
You can view which endpoints the server advertises directly on the screen using the [Find Endpoints] button — see Find Endpoints.
Discovery is Not Endpoint Search
discovery=true browses the entire node tree from the root folder and records it in the gateway log upon connection. It is not a feature for finding endpoints or automatically registering tags. To view the endpoints (security modes/policies) provided by the server, use [Find Endpoints] instead of Discovery. Since this can cause high load on servers with many nodes, keep it as false by default and find the NodeId using the method below.
Secure Connection (Channel Encryption)
This is configured in the Security (Channel Encryption) group on the connection screen. If not set to None, the edge opens a secure channel using its own client certificate and will not fall back to None even if a matching endpoint is missing.
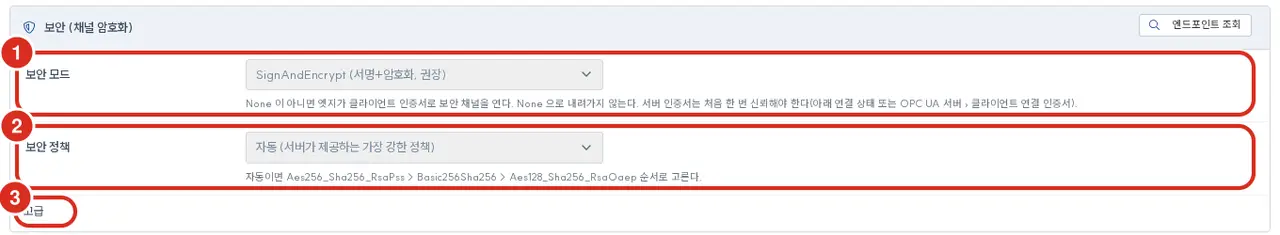
| Number | Field | Function |
|---|---|---|
| ① | Security Mode | None (암호화 없음) · Sign (서명) · SignAndEncrypt (서명+암호화, 권장) · 자동 (Sign·SignAndEncrypt 중 가장 강한 것) |
| ② | Security Policy | 자동 (서버가 제공하는 가장 강한 정책) or one of Basic256Sha256 · Aes128_Sha256_RsaOaep · Aes256_Sha256_RsaPss. Hidden if Security Mode is None |
| ③ | Advanced | Expand to see Allow deprecated policies checkbox. Enable only for legacy servers providing only Basic256 · Basic128Rsa15 (deprecated policies). This is not secure |
- Default Values — Existing connections remain as
None. New connections created via DCS/Robot cards on the add connection screen start asSignAndEncrypt. - Automatic Policy Order —
Aes256_Sha256_RsaPss>Basic256Sha256>Aes128_Sha256_RsaOaep. - Changed values must be saved to take effect.
Find Endpoints
Enter the IP, Port, and Server Name, then click [Find Endpoints]. The edge requests the endpoint list (GetEndpoints) from the server and displays it in a table. Since this does not open a session, no account is required, and it can be performed before trusting the server certificate (3-second connection limit · 6-second total limit).
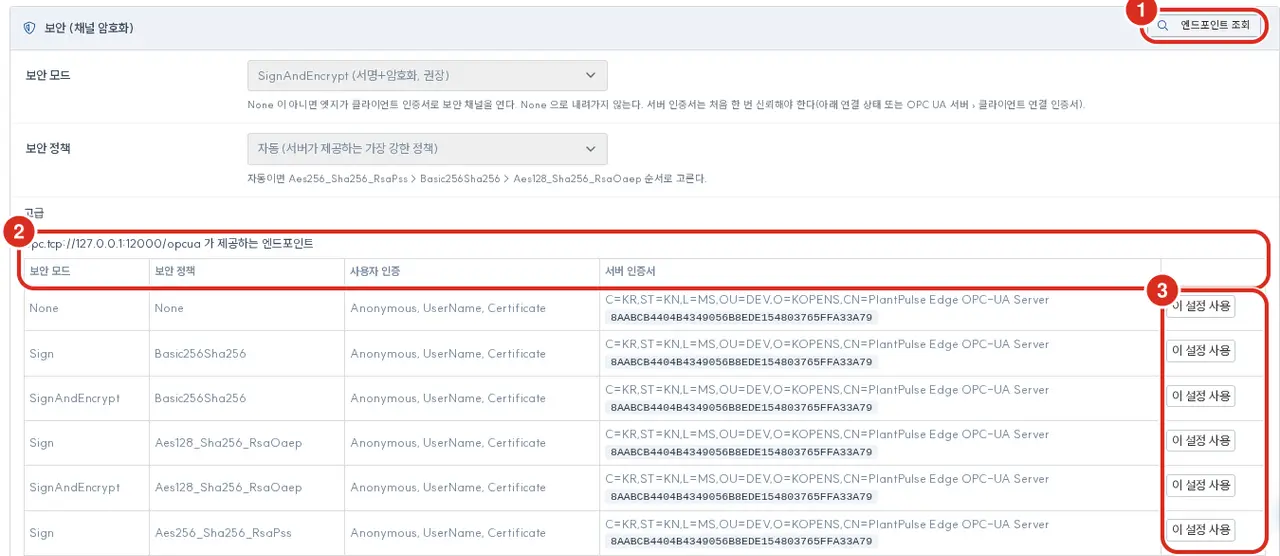
| Number | Position | Function |
|---|---|---|
| ① | Right side of group header | [Find Endpoints] — IP and Port must be entered first |
| ② | Table header | Queried address and columns — Security Mode · Security Policy · User Authentication (Anonymous · UserName · Certificate etc.) · Server Certificate (Subject and SHA-1 thumbprint) |
| ③ | End of row | [Use this setting] — Fills the security mode and policy of that row into the fields above. Must be saved to apply |
- The Deprecated Policy badge in the policy column refers to
Basic256·Basic128Rsa15. Clicking [Use this setting] for that row also enables Allow deprecated policies, and the policy field is set to Automatic instead of the specific policy. - The edge cannot connect using policies marked with the Not Supported badge.
- Even if
Certificateappears in the user authentication column, the edge only logs in via anonymous or username — see Unsupported Features.
Initial Connection — Trusting Server Certificate
The edge does not automatically trust server certificates it encounters for the first time. When connecting via a security mode for the first time, the server certificate is rejected, and the following notice appears in the security group of the connection (edit) and connection details screens.
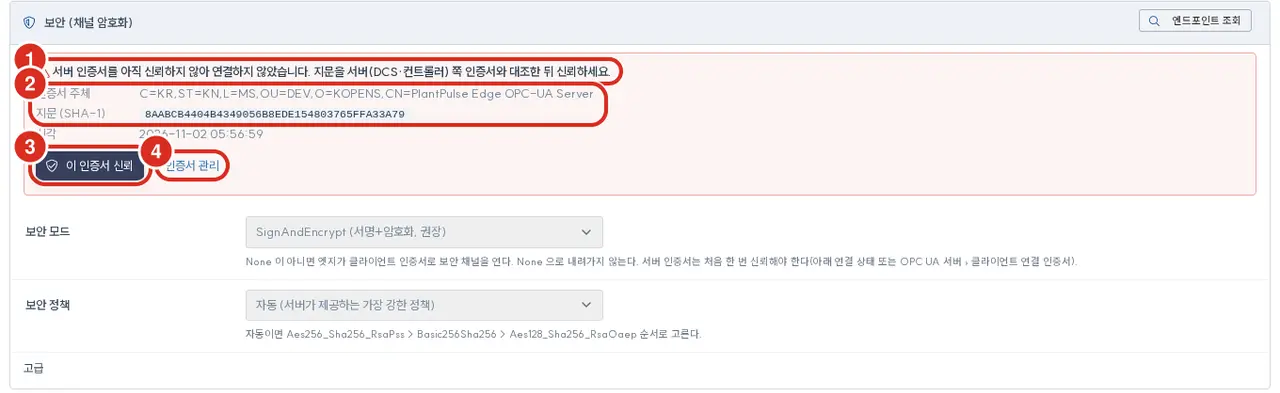
| Number | Position | Function |
|---|---|---|
| ① | First line of notice | Notice stating that the connection was not established because the server certificate is not yet trusted |
| ② | Certificate Subject · Thumbprint (SHA-1) | The certificate presented by the server. Compare the thumbprint with the certificate thumbprint on the server (DCS/controller) screen |
| ③ | [Trust this certificate] | Opens the confirmation window |
| ④ | Certificate Management | Go to OPC UA Server › Client Connection Certificates tab |
Clicking [Trust this certificate] displays the thumbprint once more in a confirmation window.
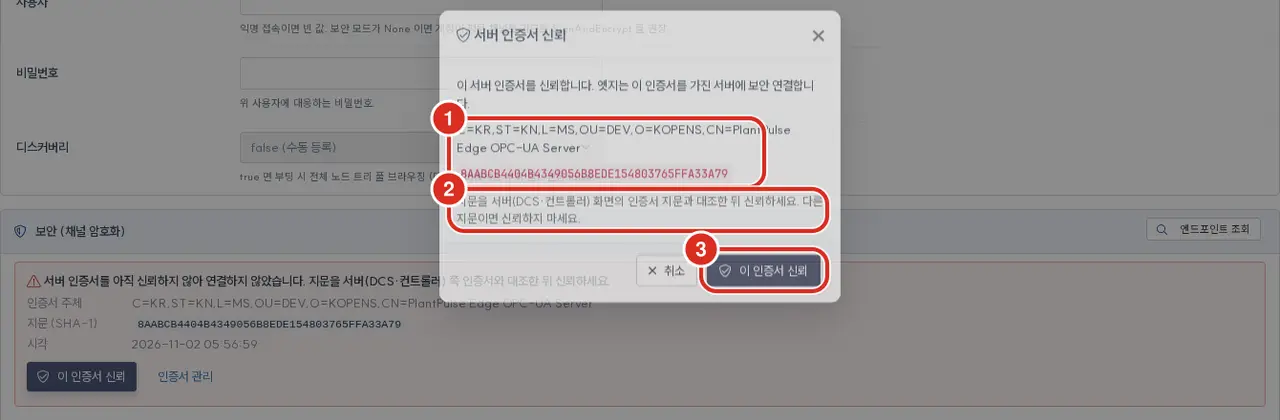
| Number | Position | Function |
|---|---|---|
| ① | Subject · Thumbprint | The certificate to be trusted. Verify it matches the thumbprint in the previous notice |
| ② | Notice | Do not trust if the thumbprint differs from the server screen |
| ③ | [Trust this certificate] | Trust the certificate. «Trusted. Reconnecting soon.» will appear |
Once trusted, the reconnection wait for the connection awaiting that certificate is released, and it reconnects soon. The notice turns green upon successful connection.
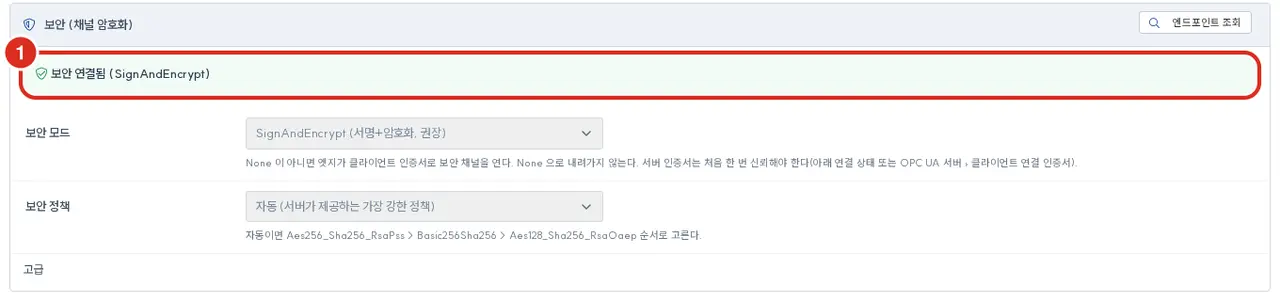
| Number | Position | Function |
|---|---|---|
| ① | Status line | «Securely Connected (SignAndEncrypt)» — The parentheses show the security mode set for the connection (Automatic is auto) |
The trust list is shared by all OPC UA connections on this edge. If multiple connections attach to the same server, you only need to trust it once.
When Server Rejects Edge Certificate
DCS and controllers often reject client certificates they encounter for the first time. In this case, the secure channel is rejected and the following notice appears.
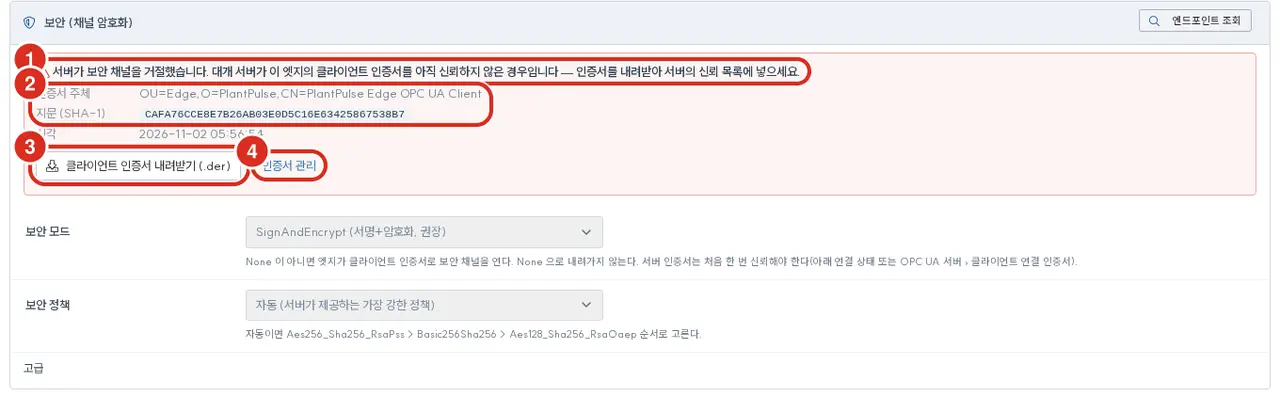
| Number | Position | Function |
|---|---|---|
| ① | First line of notice | Notice stating that the server rejected the secure channel — typically when the server does not yet trust this edge certificate |
| ② | Certificate Subject · Thumbprint (SHA-1) | The edge's client certificate. Find this thumbprint in the server's rejection list |
| ③ | [Download Client Certificate (.der)] | Downloads the edge certificate for this connection |
| ④ | Certificate Management | Go to OPC UA Server › Client Connection Certificates tab |
- Download the certificate (.der) using ③. You can also download them per connection from the «Edge's Client Certificate» section in the OPC UA Server › Client Connection Certificates tab.
- Provide the certificate to the DCS/controller administrator to add it to the server's trust list (if it is already in the rejection list, it can be moved to the trust list). Follow the server manufacturer's manual for the procedure.
- The edge will reconnect on the next connection attempt.
Certificate Management — OPC UA Server › Client Connection Certificates
You can view all certificates used by the edge as a client in one place under the Client Connection Certificates tab of the OPC UA Server screen (/ui/opcua). This is separate from the certificates for the OPC UA server that the edge provides to SCADA (found in the Client Certificates tab).
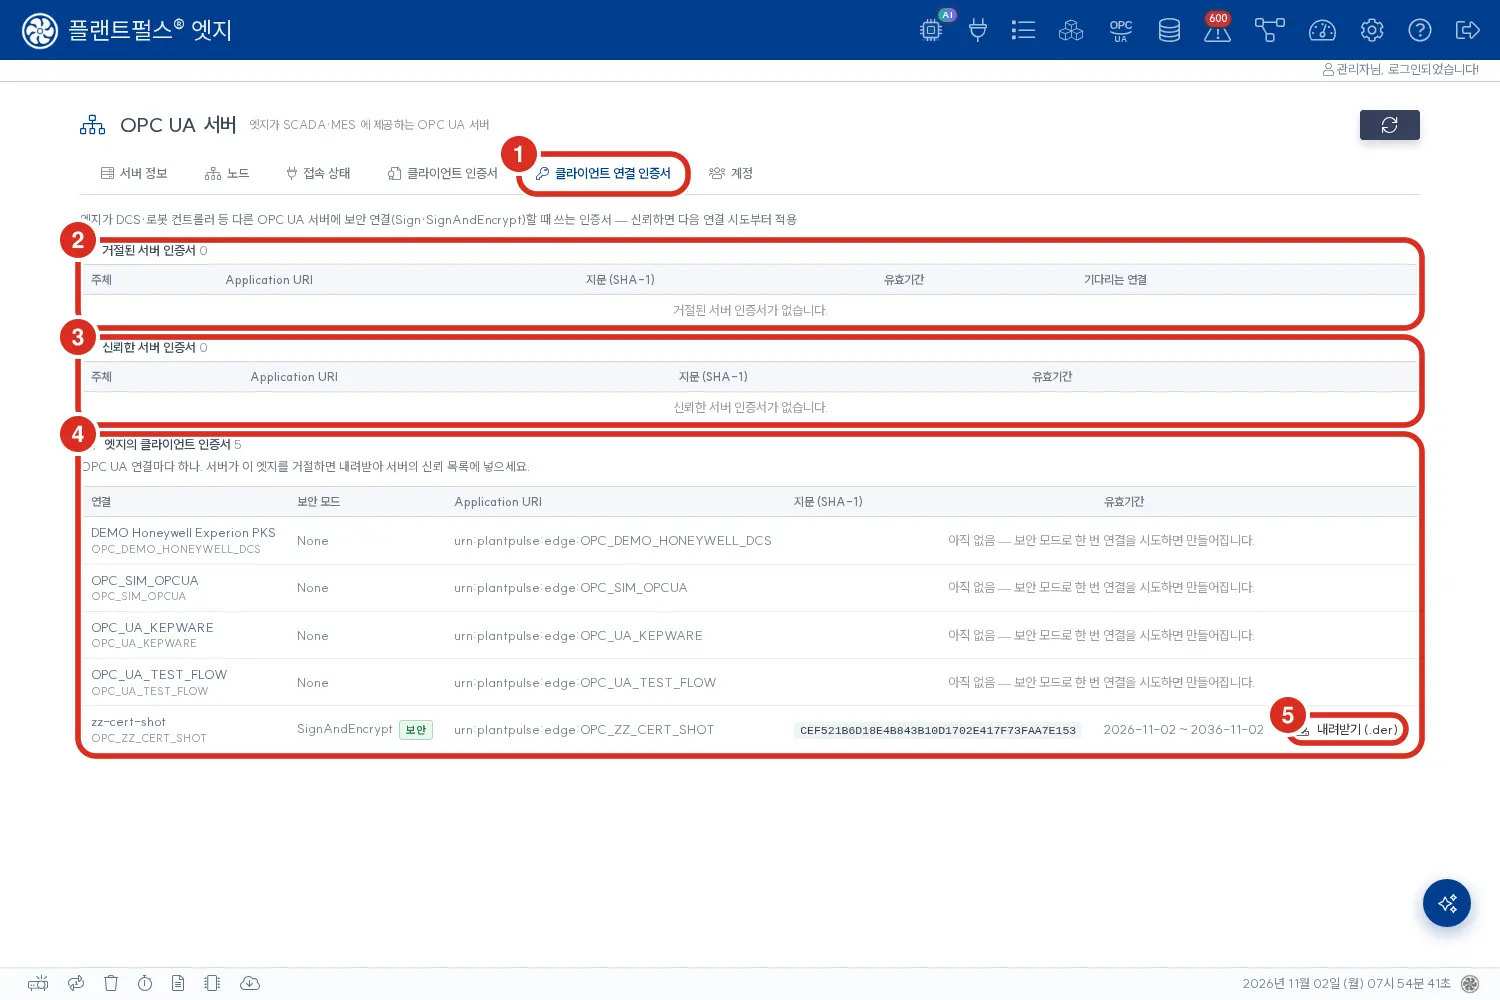
| Number | Position | Function |
|---|---|---|
| ① | Tab | Client Connection Certificates |
| ② | Rejected Server Certificates | Server certificates rejected by the edge — Subject · Application URI · Thumbprint · Validity · Waiting Connection. [Trust] or [Delete] |
| ③ | Trusted Server Certificates | Server certificates trusted by the operator. [Untrust] moves the certificate back to the rejection list, and the edge will stop connecting to that server from the next attempt |
| ④ | Edge's Client Certificates | One per OPC UA connection — Connection · Security Mode · Application URI · Thumbprint · Validity. Connections that have never attempted a secure connection show «None yet» |
| ⑤ | [Download (.der)] | The edge certificate for that connection. Used when adding to the server's trust list |
- Rejected certificates that are [Deleted] will reappear if a connection to the same server is attempted again.
- If you [Untrust] a certificate, existing open connections will be terminated upon the next reconnection attempt.
Edge's Client Certificate
| Item | Value |
|---|---|
| Type | Self-signed, RSA 2048 |
| Validity | 10 years. When expired, a new one is created and must be re-trusted by the server |
| Creation Timing | When the connection first attempts to connect via a security mode |
| Application URI | urn:plantpulse:edge:<OPC ID> — Unique per connection |
| Storage Location | /data1/pp-data/opcua-client ($PE_DATA_DIR/pp-data/opcua-client). The trust list is also stored here |
- Even if a connection is deleted, the certificate remains; recreating the connection with the same OPC ID will reuse that certificate. There is no need to re-trust it on the DCS.
- This directory is a target for Backup. Restoring it recovers both edge certificates and the trust list.
Unsupported Features
- X.509 User Certificate Login — User authentication is supported only via anonymous or username + password.
- CA-Signed Client Certificates — Edge certificates use self-signing only.
- Trust List Replication for HA Pair Boxes — Trust lists are separate for each box. In an HA configuration, trust the server certificate on each box, and add the edge certificate for each box to the server.
Tag PLC Address Notation
OPC-UA tag addresses typically use the following format called NodeId.
| Notation | Description |
|---|---|
ns=2;s=Channel1.Device1.Tag1 | namespace 2, string identifier — Most common in Kepware |
ns=2;i=1234 | namespace 2, numeric identifier |
ns=3;g=09087e75-8e5e-499b-954f-f2a8624db28a | GUID format |
ns=is the namespace number. Usually2.- Following
s=, a path such as “Channel.Device.Tag” is entered (the path as created in Kepware).
How to find the NodeId
- Mapping tables are often found in PLC manufacturer / Kepware manufacturer manuals.
- Using a free OPC-UA client like UA Expert, you can connect directly and right-click a node in the tree to copy the NodeId.
- The same can be achieved using Kepware's own OPC Quick Client tool.
Kepware Quick Setup
This is the procedure based on Kepware, a frequently used combination.
- Kepware Server → Project → Add Channel (e.g.,
Simulator) - Add Device (e.g.,
Simulator) → Model =16 Bit Device - Add Tag → Name
Sine1, typeFloat, scan rate100ms - In Project Properties → OPC UA → Server Endpoint, enable port
49320 - Select the Security Policies for the server endpoint. For secure connections, enable
Basic256Sha256or higher and Sign and Encrypt, and add the edge certificate to Kepware's trust list — see When Server Rejects Edge Certificate. - Enable anonymous or user account
In the registration form of this gateway:
| Field | Value |
|---|---|
| IP | IP of Kepware server PC |
| Port | 49320 |
| User/Password | Account created above (blank if anonymous) |
| Tag PLC Address | ns=2;s=Simulator.Simulator.Sine1 |
Common Problems and Troubleshooting
| Symptom / Message | Possible Cause | Solution |
|---|---|---|
| “Connection refused” / No connection | OPC-UA server is off or port is blocked | Verify OPC-UA server is running and IP/Port are correct |
| “User access denied” | User/password error, or anonymous access not allowed on server | Register user on server or allow anonymous access |
Connection fails while Security Mode is None, log shows no SecurityMode=None endpoint | Server does not have None endpoints open | Change Security Mode to Sign or SignAndEncrypt and verify with [Find Endpoints] |
Connected but values are always 0 or null | Tag NodeId typo, namespace number mismatch | Verify the NodeId actually works using UA Expert etc. |
| Frequent disconnection and reconnection | Network instability or server PC load | Inspect server PC resources / cables / switches |
Secure Connection Errors (Screen Text)
If a secure connection fails, the following messages appear in the security group of the connection and connection details screens. These appear in both Korean and English.
| Code | Screen Text (ko) | Screen Text (en) | Solution |
|---|---|---|---|
OPCUA_SERVER_CERT_UNTRUSTED | 서버 인증서를 아직 신뢰하지 않아 연결하지 않았습니다. 지문을 서버(DCS·컨트롤러) 쪽 인증서와 대조한 뒤 신뢰하세요. | Not connected: the server certificate is not trusted yet. Compare the thumbprint with the server's (DCS / controller) certificate, then trust it. | Compare thumbprints and [Trust this certificate] |
OPCUA_SERVER_CERT_INVALID | 신뢰한 서버 인증서가 유효하지 않습니다(만료·폐기·용도 불일치). 서버 쪽 인증서를 확인하세요. | The trusted server certificate is not valid (expired, revoked or wrong usage). Check the server's certificate. | Issue a new server certificate and trust the new thumbprint |
OPCUA_CLIENT_CERT_REJECTED | 서버가 보안 채널을 거절했습니다. 대개 서버가 이 엣지의 클라이언트 인증서를 아직 신뢰하지 않은 경우입니다 — 인증서를 내려받아 서버의 신뢰 목록에 넣으세요. | The server refused the secure channel - usually it does not trust this edge's client certificate yet. Download it and add it to the server's trust list. | Add edge certificate (.der) to the server's trust list |
OPCUA_PKI_DIR_MISSING | 엣지의 클라이언트 인증서 저장소를 찾지 못했습니다(데이터 볼륨 PE_DATA_DIR 를 확인하세요). | The edge's client certificate store is missing (check the data volume PE_DATA_DIR). | Verify if the data volume (/data1) is mounted |
OPCUA_PKI_ERROR | 엣지의 클라이언트 인증서 저장소를 읽거나 만들지 못했습니다. 서버 로그를 확인하세요. | The edge's client certificate store could not be read or created. See the server log. | Check /data1/pp-data/opcua-client permissions and disk space |
OPCUA_SECURITY_CONFIG_INVALID | 보안 모드·정책 설정이 올바르지 않습니다(폐기된 정책은 '낡은 정책 허용'을 켜야 합니다). | The security mode / policy setting is invalid (a deprecated policy needs 'Allow deprecated policies'). | Verify security mode/policy values. If deprecated, enable «Allow deprecated policies» |
OPCUA_NO_MATCHING_ENDPOINT | 서버가 설정한 보안 모드·정책·인증 방식에 맞는 엔드포인트를 제공하지 않습니다. [엔드포인트 조회]로 확인하세요. | The server offers no endpoint with this security mode, policy and user token. Check with [Find endpoints]. | Select a combination provided by the server in [Find Endpoints] and click [Use this setting] |
OPCUA_CONNECT_FAILED | 연결하지 못했습니다(네트워크·시간 초과·세션). | Could not connect (network, timeout or session). | Verify IP, Port, Firewall, and server operational status |
Frequently Used Data Types
| PLC Value | Data Type | Format Auxiliary | PLC Address Example |
|---|---|---|---|
| On/Off | Boolean | (Blank) | ns=2;s=Pump.Status |
| Integer | Integer | (Blank) | ns=2;s=Counter |
| Large Integer | Long | (Blank) | ns=2;s=Total |
| Float (32-bit) | Float | (Blank) | ns=2;s=Pressure |
| Float (64-bit, Precise) | Double | (Blank) | ns=2;s=PrecisionTemp |
| String | String | (Blank) | ns=2;s=Recipe.Name |
For OPC-UA, the format column is typically left blank (the server provides the data type).
Further Examples / Automated Registration
For automated registration using scripts or APIs, please refer to the OPC-UA examples on the Advanced — REST API page.