OPC UA Server
The gateway has a built-in OPC-UA server, which exposes collected tag values directly to external OPC-UA clients (SCADA, HMI). This page covers the built-in server's connection information · security settings, node tree (tag list + real-time values + time series), connection status, client certificates, client connection certificates, and accounts across six tabs on a single screen.
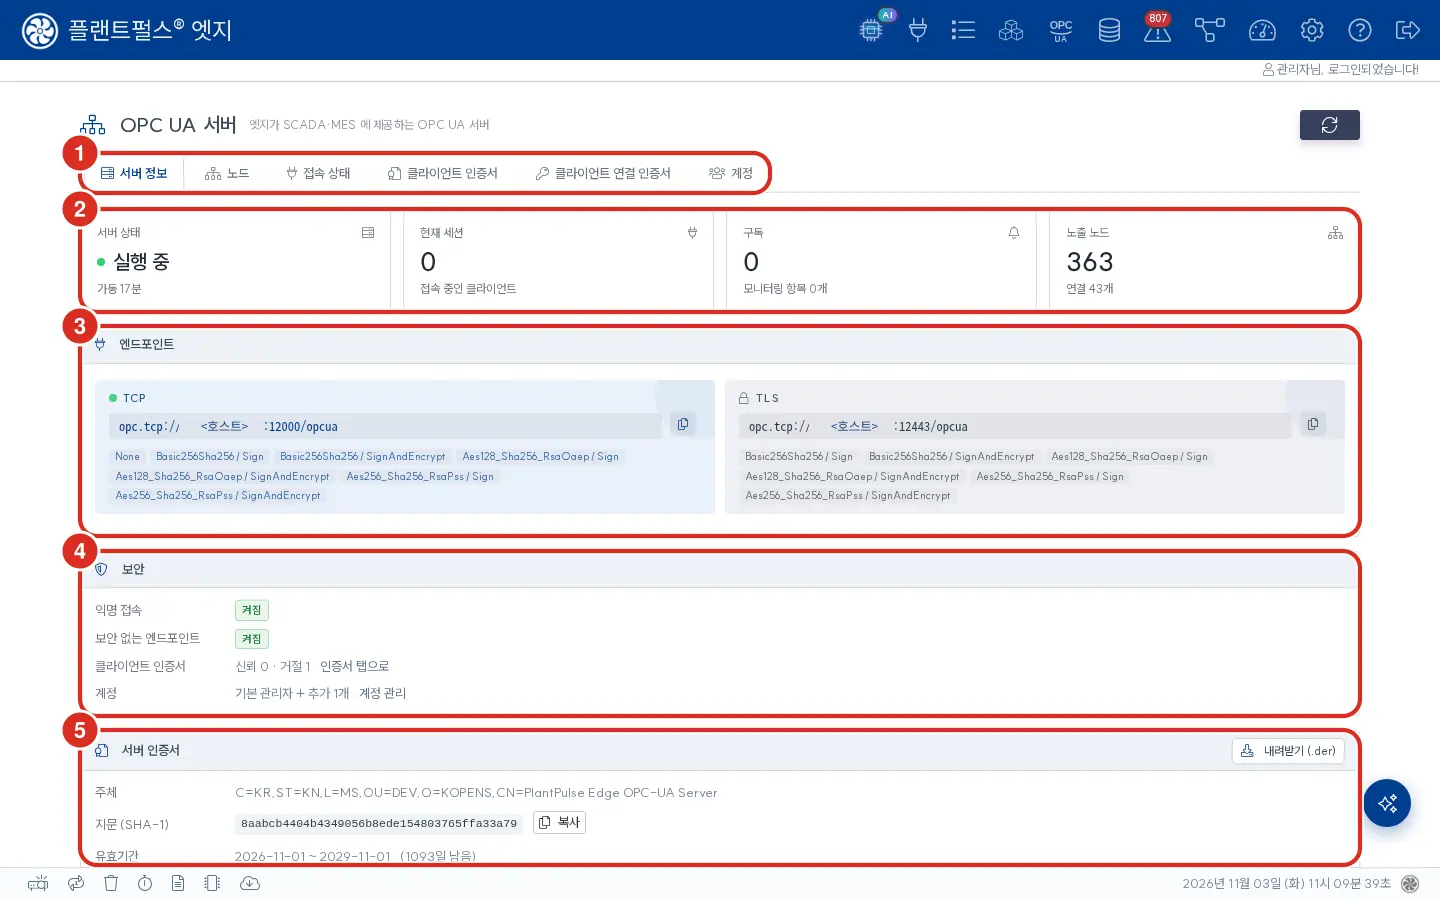
| No. | Location | Content |
|---|---|---|
| ① | Tab Row | Six tabs |
| ② | Status Card | Server status · sessions · subscriptions · number of exposed nodes |
| ③ | Endpoint | TCP / TLS connection URL and provided security policies |
| ④ | Security | Anonymous connection · insecure endpoint · client certificates · accounts |
| ⑤ | Server Certificate | Subject · fingerprint · expiration date, [Download (.der)] |
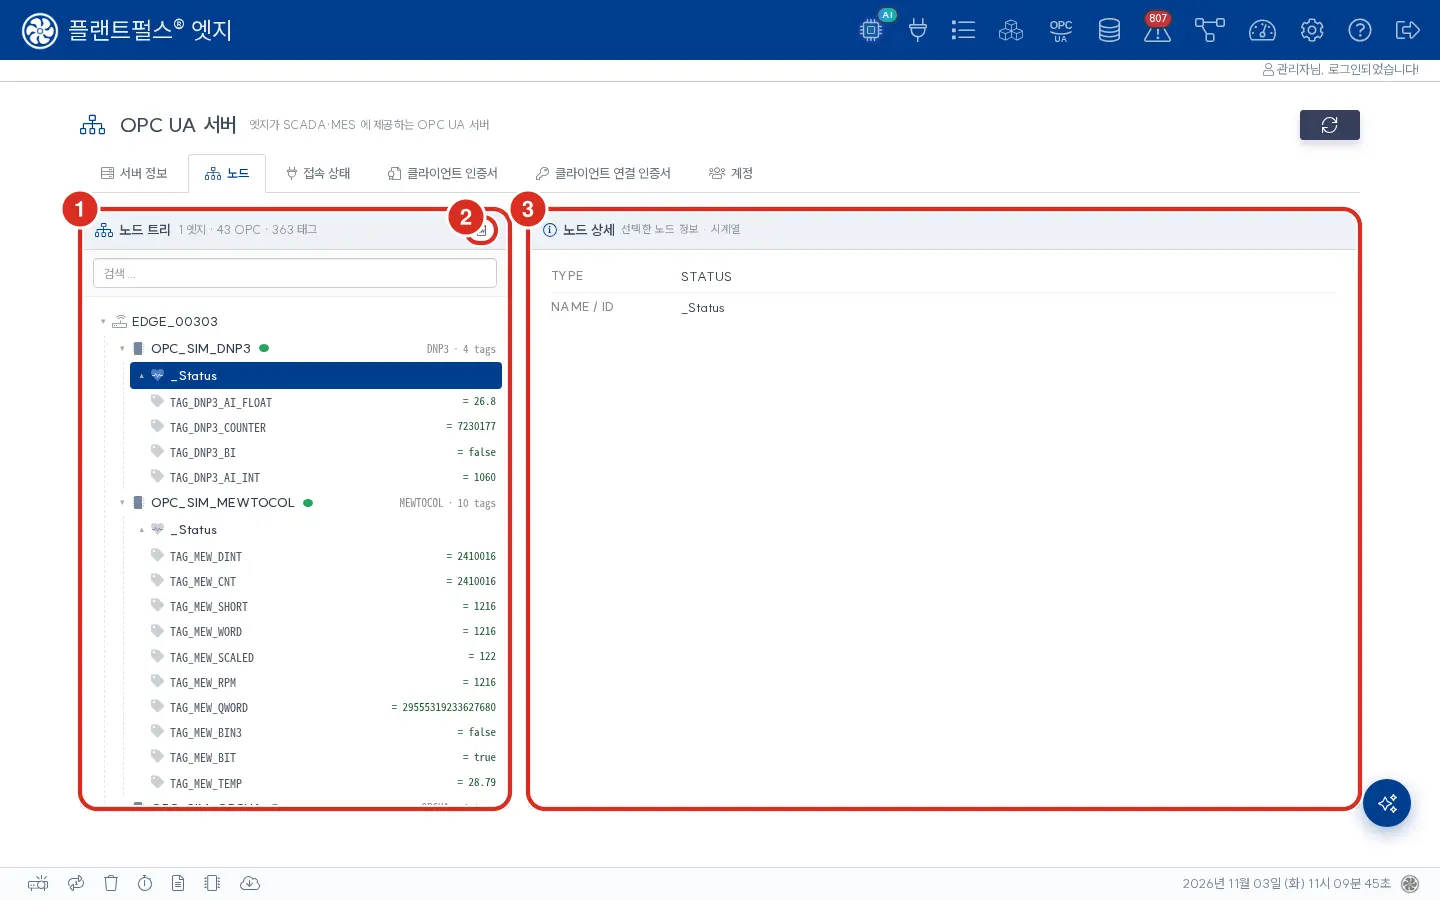
| No. | Location | Content |
|---|---|---|
| ① | Node Tree | 엣지 → OPC → 태그, connection status dot and latest value |
| ② | Panel Header | CSV icon — download address space |
| ③ | Node Details | Information and time series of the selected node |
- Implementation: Eclipse Milo 1.1.8
- Transport:
opc.tcponly (UA Binary). Endpoint paths:/opcua—opc.tcp://<호스트>:12000/opcua(TCP port) ·opc.tcp://<호스트>:12443/opcua(«TLS» port). 12443 is also opc.tcp with a security policy, not HTTPS. - Security policies: Basic256Sha256 / Aes128_Sha256_RsaOaep / Aes256_Sha256_RsaPss — Sign · SignAndEncrypt for both ports.
- None (Insecure): When
opc.ua.server.security.none=yes(default), session endpoints are open only on the TCP port. By specification, Discovery (/opcua/discovery) is always None, but sessions cannot be opened. - User token: Anonymous (
opc.ua.server.anonymous=yes, default) / UserName+Password / X.509 (only certificates in the server trust list) - Server certificate: Created as self-signed (RSA 2048) upon first boot and stored in
$PE_DATA_DIR/pp-data/opcua/— the same certificate and trust list are maintained after upgrades. - PubSub: Not supported — use Sparkplug B for publishing.
Navigate to the OPC UA Server icon in the left menu or go directly to http://<gateway>/ui/opcua.
1. Screen Configuration
The screen is divided into six tabs in the header. Adding #server · #nodes · #sessions · #certs · #client-certs · #accounts to the end of the URL opens that specific tab; otherwise, the last viewed tab in the browser opens.
| Tab | Content |
|---|---|
| Server Info | Server status · uptime, current sessions · subscriptions · number of exposed nodes. TCP / TLS endpoint URLs for external clients (copy button) and security policy badges actually provided by each endpoint. Toggle for anonymous connection · insecure endpoint, number of client certificates · accounts, server certificate (subject · SHA-1 fingerprint · expiration · key). |
| Node | Left node tree (엣지 → OPC → 태그, connection status dot for each OPC (status name on hover), tag count, latest value of each tag) and right node details (meta + real-time value + time series chart for numeric/boolean tags). Download the address space via the CSV icon in the panel header. |
| Connection Status | Number of current sessions · subscriptions · monitored items, number of rejected connections, session list. |
| Client Certificate | Rejected · Trusted lists of client certificates that attempted a secure channel, [Trust] [Move to Rejected] [Delete], server certificate [Download (.der)]. |
| Client Connection Certificate | Certificates used when the Edge connects to an external OPC UA server as a client. Refer to OPC UA Protocol. |
| Account | Management of the default administrator + additional accounts (Read-only / Read-Write). |
The host for the endpoint URL is opc.ua.server.domain. If this value is a loopback (127.0.0.1 · localhost · 0.0.0.0, installation default), the URL is generated based on the host the browser connected to — preventing a copied URL from pointing to the local PC.
2. NodeId Convention
Each tag is exposed as an OPC-UA NodeId as follows. The root of the address space is the Edge ID (Objects below), followed by the OPC (connection) folder, and then the tags.
ns=2;s=<EDGE_ID>.<OPC_ID>.<TAG_ID>
Example: ns=2;s=EDGE_00303.OPC_00303.TAG_TEST_00042
- If a tag has a tag group, it is placed under the
GROUP.<그룹>folder beneath the OPC folder, but the tag's NodeId remains in the format above. - Each OPC folder contains a
_Statusfolder and providesConnected·State·LastError·LastCollectedAt·CycleMsevery 2 seconds (read-only). - If
edge.idis empty or not in the format ofEDGE_+ uppercase letters · numbers ·_, the OPC-UA server will not start without generating a name (ERROR log).
The NodeId in previous versions was EDGE.<SITE_ID>.<OPC_ID>.<TAG_ID>. Now, the root is the Edge ID and there is no site hierarchy. Since there are no compatibility aliases, SCADA-side NodeIds must be re-mapped after the upgrade.
External clients (UaExpert, KEPServerEX, Ignition, etc.) can subscribe directly using this NodeId. A copy button next to the NodeId in the details panel allows for easy copying to the clipboard.
3. Node Tree — Search / Refresh
- Entering text into the search bar at the top of the tree filters tree, OPC, and tag names by real-time partial match. If a match exists in a descendant, the parents (OPC, Edge) are automatically expanded.
- Refresh (↻) button in the header — re-fetches information for the tree and each tab. This is rarely needed as data typically updates automatically.
- Subtrees can be collapsed/expanded using the ◂/▾ toggle on each row. When search is active, nodes are automatically expanded for matching and restored to their previous toggle state when the search is cleared.
- Automatic shortening of long values (ellipsis) — if the current value of a tree node exceeds the column width, it is processed as
text-overflow: ellipsiswith…. The full plain text is shown in a tooltip on hover — a protection mechanism to prevent JSON / long STRING values from breaking the tree layout.
Values displayed in the tree are automatically updated every 2 seconds while the node tab is visible (/ui/opcua/tree). The tree structure, expansion state, right details, and charts are maintained.
4. Node Details + Time Series Chart
Clicking a tag row displays the following on the right:
- NodeId (copyable)
- Tag ID / DataType / PLC Address / Alias / Description
- Value (current value + last update time, up to ms)
- Status (
OK/ERROR (메시지))
The chart type changes automatically based on the value type.
4.1 Numeric / Boolean (ECharts Line Chart)
If the value is numeric (Integer/Long/Float/Double, etc.) or boolean, an ECharts time series line chart is drawn.
| Chart Feature | Description |
|---|---|
| Range Selection | Select 1분/5분/10분/30분/1시간(default)/3시간/12시간/24시간 from the combo box at the top right of the chart — immediately fetches and redraws historical data from Cassandra (tm_tag_point) |
| dataZoom Slider | Grey-toned drag bar at the bottom of the chart — horizontal zoom / pan |
| Auto-addition | 2-second interval polling adds new values to the chart |
| Tooltip | Time in ms + value on mouse over |
| Boolean | Visualizes 0/1 toggle in a step end (step-like) format |
| Sampling | Holds up to 5,000 points; oldest points are removed first when exceeded (lttb downsampling) |
4.2 STRING (vis-timeline Box Chart)
If the value is a STRING, a vis-timeline range box chart is drawn instead of an ECharts line chart — this highlights state change points by grouping consecutive identical values into a single box.
| Item | Description |
|---|---|
| Box = Consecutive identical value interval | Example: if "RUNNING" is maintained from 12:00 to 12:35, it is shown as one box for that interval |
| Box Color | Automatic based on value hash — identical text always has the same color |
| Box Label | Plain text value (full text on hover if long) |
| Time Axis Zoom/Pan | Basic vis interaction (mouse wheel / drag) |
| Update | Polling reorganizes the entire dataset by sorting history in ASC order (no flickering if there is little change) |
| Node Change | Instance destroy via disposeStringTimeline() + regeneration of the new node's chart |
STRING charts are suitable for viewing non-numeric time series, such as state machine logs (
READY → RUNNING → ERROR → IDLE), at a glance. The same tone is also applied to View Tag Value Trend (tag-view).
5. Edge System Tags
A system connection named OPC_SYSTEM_<EDGE_ID> is automatically visible in the tree. This is a collection of 38 system tags exposing the gateway's own status as OPC-UA nodes, with tag IDs from TAG_<EDGE_ID>_90000 to TAG_<EDGE_ID>_90037.
Representative tags:
| Tag Name | Meaning |
|---|---|
THREAD_COUNT | JVM thread count |
TAG_COUNT | Total number of registered tags |
SERVER_STARTED_TIMESTAMP | Edge boot time (epoch ms) |
PLC_CON_CONNECTED_COUNT | Number of currently active connections (OPC) |
MEMORY_USED_PERCENT | Memory usage (%) |
The connection status of the system connection is always displayed as CONNECTED (as it is itself and has no connection concept), and there is no _Status folder.
6. Using with External Clients — Flow
- Copy the endpoint URL from the Server Info tab (e.g.,
opc.tcp://<gateway>:12000/opcua). Connection will fail if the path/opcuais omitted — the server will reject the HELLO withBadTcpEndpointUrlInvalid. - In an OPC-UA client such as UaExpert / KEPServerEX, add a new server → enter the URL → select a security policy.
- If insecure endpoint is enabled, you can connect via the TCP port using
None. - When connecting with a security policy (e.g., Basic256Sha256), the server initially rejects the client certificate. Compare the fingerprint in the Rejected list of the Client Certificate tab with the SCADA certificate and click [Trust] — this applies to the next connection without requiring a restart. If the client also needs to trust the server certificate, use [Download (.der)] to provide it.
- If insecure endpoint is enabled, you can connect via the TCP port using
- Authentication modes:
- Anonymous — connects directly if Anonymous Connection is enabled in the Server Info tab. Anonymous sessions are read-only.
- Username / Password — default administrator (
opc.ua.server.user/opc.ua.server.password) or additional accounts from the Account tab. - X.509 — accepts only certificates in the server trust list.
- After connecting, subscribe to tags using the NodeId
ns=2;s=...format.
7. Accounts · Writing
- The default administrator (
opc.ua.server.user/password) has Read-Write permissions and cannot be deleted from the screen. The password can be changed in the settings screen. - Create additional accounts in the Account tab — IDs must start with English letters or numbers and contain only English letters, numbers, and
._-, up to 64 characters (default admin ID cannot be used); passwords must be 8–128 characters. Permissions are Read-only / Read-Write. Permission changes apply immediately to open sessions; deletion, disabling, or password changes terminate the account's session. - When a non-anonymous session (default admin · read-write account · trusted X.509 certificate) writes to a tag node, the value is transmitted to the corresponding PLC (same flow as driver write, with account · security policy · connection IP recorded in
tm_tag_write). The node value changes only when the PLC write is successful. - Reasons for rejected writes:
| Result | Cause |
|---|---|
Bad_NotWritable | Read-only tag (client_access=R) — for everyone |
Bad_UserAccessDenied | Anonymous session, read-only account, or this edge lacks PLC write permission in an HA pair |
Bad_InternalError | PLC write failed, or write path is not yet ready during boot |
Both opc.ua.server.anonymous and opc.ua.server.security.none are default yes. In this state, any client on the network can read all tags without a certificate or password (though writing by anonymous sessions is blocked). For production networks, disable Allow Anonymous Connection and Insecure Endpoint in the OPC UA Server tab of the settings screen.
8. Troubleshooting
| Symptom | Checkpoints |
|---|---|
| OPC not visible in tree | Whether 자주 하는 작업 → 새 PLC 연결 추가 is complete, or if the gateway's Auto-start Collection option for that OPC is enabled |
Value next to tag shown as - | The tag has never been updated. Check collection start / OPC connection / Quality |
Client connection failure with BadTcpEndpointUrlInvalid | Missing /opcua at the end of the endpoint URL |
| Visible in tree but external client cannot find NodeId | Typo, or using NodeId in EDGE.<SITE_ID>... format from before 2026.11 (§2) |
| Server Info tab shows «Stopped» | edge.id is empty or formatted incorrectly, or failed to obtain PE_DATA_DIR — both cases prevent the server from starting and leave an ERROR log |
| Rejected when connecting via security policy | Client certificate not yet trusted — click [Trust] in Client Certificate tab |
Unable to connect via None | Insecure Endpoint is disabled or attempting to connect via port 12443 (None sessions only on TCP port) |
Writing results in Bad_NotWritable / Bad_UserAccessDenied | Refer to §7 table |
| Chart is empty | Cassandra history for the tag does not exist yet (newly registered tag) — points will be added shortly |
| Chart looks jagged | Increasing the range to 24 hours applies automatic downsampling for a smoother view |
| Client does not trust server certificate | Self-signed certificate from the gateway — "Trust" it in the client or import the certificate downloaded via [Download (.der)] |
9. Learn More
- Node-RED (
/ui/flow) — Process/send the same tag values via flows. Refer to자주 하는 작업 → Node-RED 로 자동화 / IIoT 플로우. - REST API — Fetch the same data directly via HTTP. Refer to
고급 / 통합 파트너용 → REST API. - Driver Technical Reference → OPC-UA — Describes the gateway's OPC-UA client side (the path for connecting to external OPC-UA servers to fetch data).