Security Management
Table of Contents
- Overview
- Screen Layout — 3 Sub-menus
- User Screen
- Security Policy Screen
- API Authentication Token Screen
- Use Case Scenarios
- FAQ
- Related Screens
Overview
The security management items in the System group manage three components: user accounts, security policies (additional permission groups beyond roles), and API authentication tokens (keys used by external systems to call Platform APIs). The User and API Token menus are visible only to ADMIN, while the Security Policy menu is visible to both ADMIN and API. None of these are visible to USER.
This screen is used for the following tasks:
- Issuing new operator accounts, editing, or deleting existing user information
- Assigning security policies to users
- Issuing tokens, restricting IPs, and deploying them so that external systems (MES, ERP, etc.) can call Platform APIs
Path: Left Menu > System > User / Security Policy / API Token
Screen Layout — 3 Sub-menus
| Sub-menu | URL | Purpose |
|---|---|---|
| User | /user/index | Manage user accounts capable of logging into the system |
| Security Policy | /security/index | Manage permission groups (security policies) that can be assigned to users |
| API Authentication Token | /token/index | Issue, IP-restrict, and deploy authentication tokens for external API calls |
Each sub-menu consists of a list screen (index.jsp) and a form screen (form.jsp). Clicking add/edit for an item in the list navigates to the form screen.
User Screen
Path: Security > User (/user/index)
The top of the page contains the title "User" and a red Add User button on the right.
User List Table
┌──────────────────────────────────── 목록 ────────────────────────────────────┐
│  - │ 로그인 ID │ 이름 │ 팀명 │ 이메일 │ 전화 │ 역할 │ 보안정책 │ 등록일 │ 마지막 수정일 │ 액션 │
└─────────────────────────────────────────────────────────────────────────────┘
| Column | Width | Alignment | Display |
|---|---|---|---|
| Check/Select | 40px | Center | Row selection (Active/Inactive based on operating environment) |
| Login ID | 120px | Center | ID used by the user for login |
| Name | 100px | Center | Display name |
| Team Name | Auto | Center | Affiliated team (address field — displayed as "Team Name" label in the form) |
| 200px | Center | Email address | |
| Phone | 200px | Center | Mobile phone number |
| Role | 80px | Center | One of ADMIN / API / USER |
| Security Policy | 120px | Center | Assigned security policy name (empty if none) |
| Registration Date | 150px | Center | Account registration time |
| Last Modified Date | 150px | Center | Time of last information modification |
| Action | 80px | Center | Edit/Delete buttons |
Add/Edit User Form
Navigate to the form screen via the Add User button at the top or the action buttons in the list.
1) Login fieldset
| Input | Path | Width | Note |
|---|---|---|---|
| Login ID | user_id | 200px | English/Numbers/Underscore recommended |
| Password | password | 200px | Displayed only during new registration (mode='I'). Input field is hidden in edit mode for security — password changes follow a separate flow |
| Role | role | 200px | Selector — ADMIN/API/USER (Security field toggles automatically upon change) |
| Security | security_id | 200px | Selector — Select from registered security policies (Visible when the role is a specific case such as API. toggleSecurityField()) |
2) Basic Information fieldset
| Input | Path | Width | Placeholder |
|---|---|---|---|
| Name | name | 200px | — |
email | 200px | — | |
| Mobile Phone | phone | 200px | "Please enter only numbers for the mobile phone number. e.g.) 0104125678" |
| Team Name | address | 450px | — |
3) Additional Attributes fieldset
| Input | Path | Width |
|---|---|---|
| Note | attr_01 | 800px × 150px (Text area) |
Form Submission
| Button | Position | Action |
|---|---|---|
| List(☰) | Left | index() — Return to user list screen |
| Save | Right (Blue, 100px) | saveEvent() — Save after input validation |
User Role Definitions
| Role | Label | Description |
|---|---|---|
| ADMIN | System Administrator | Access to all menus. Can change users, security policies, and system settings |
| API | API Developer | Account for API calls. Security policy assignment is mandatory. In the console, all menus are visible except User and API Token |
| USER | General User | Only Asset, Tag, Data Inquiry, Maintenance, ISO Data, and Alarm menus are visible. No write permissions in the console (except for individual alarm confirmation) |
For a detailed menu breakdown by role, refer to the Permissions and Menu Exposure table.
Role changes are applied immediately, but if a user is already logged in, the new role will be applied upon the next login.
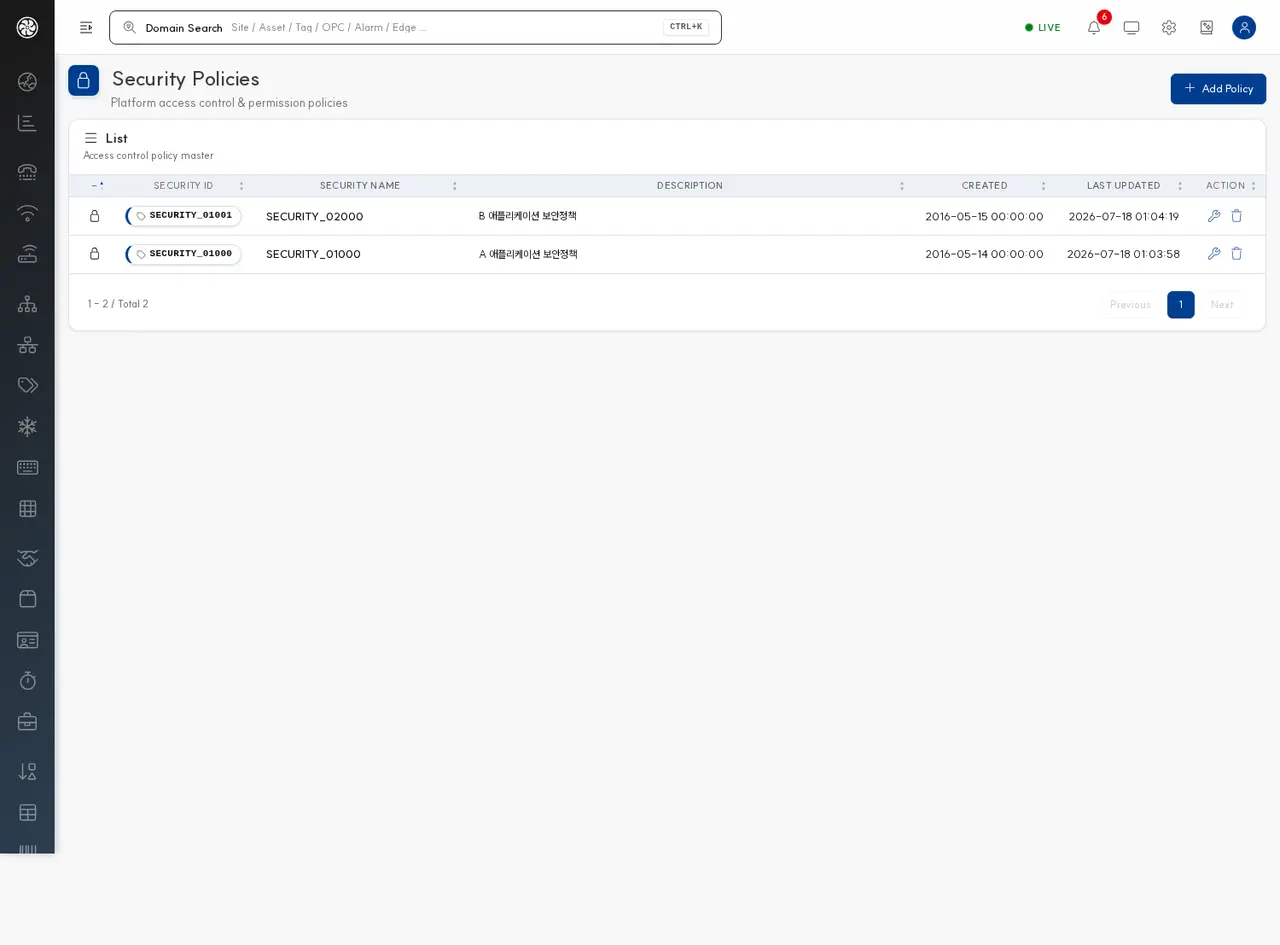
Security Policy Screen
Path: Security > Security Policy (/security/index)
The top of the page contains the title "Security Policy" and a red Add Security button on the right.
Security Policy List Table
┌────────────────────────────── 목록 ──────────────────────────────┐
│  - │ 보안 ID │ 보안명 │ 설명 │ 등록일 │ 마지막 수정일 │ 액션 │
└──────────────────────────────────────────────────────────────────┘
| Column | Width | Display |
|---|---|---|
| Check/Select | 40px | Row selection |
| Security ID | 150px | System-assigned identifier (e.g., SECURITY_00001) |
| Security Name | 250px | Human-readable name (Only English/Numbers/_ allowed) |
| Description | Auto | Note on policy purpose |
| Registration Date | 150px | Policy registration time |
| Last Modified Date | 150px | Policy last modification time |
| Action | 80px | Edit/Delete buttons |
Security Policy Form
1) Basic Information fieldset
| Input | Path | Width | Note |
|---|---|---|---|
| Security ID | security_id | 200px | Read-only — Automatically assigned by the system |
| Security Name | security_name | 300px | Placeholder: SECURITY_NAME_00001 (영문 및 숫자, _ 만 입력) |
| Description | description | 500px | Free text (Until 2026.09, the name was security_desc) |
2) Permissions fieldset
Detailed permission granting (Object permission UI by asset unit) was deactivated as of 2026-03-21. Currently, security policies only register and manage Name + Description, and actual permission application operates based on the user's role (ADMIN/API/USER).
Form Submission
| Button | Position | Action |
|---|---|---|
| List(☰) | Left | Return to security policy list screen |
| Save | Right (Blue, 100px) | Save after input validation |
API Authentication Token Screen
Path: Security > API Authentication Token (/token/index)
An API authentication token is a key used by external programs (MES/ERP/integration tools, etc.) to call Platform APIs. Security can be enhanced by restricting the allowable IP ranges for each token.
Token List Table
The top of the page contains the title "API Authentication Token" and two red buttons: Add API Token and Refresh. An API Token Deployment button (120px) is located on the right side of the list panel header.
| Column | Width | Display |
|---|---|---|
| Check/Select | 40px | Row selection |
| Auth Token | 380px | Issued token string (16+ characters) |
| Login ID | 200px | User ID that was issued the token |
| Allowable IP | 200px | IP pattern permitted for token use |
| Description | Auto | Token purpose |
| Action | 80px | Edit/Delete buttons |
Add/Edit Token Form
Navigate to the form screen using the Add API Token button at the top.
Guidance Message (Blue Box)
ℹ️ API 인증 토큰 도움말
  API 인증 토큰은 API를 통해 플랫폼에 명령과 데이터 조회 등에 사용할 수 있는 보안 토큰입니다.
  • 접근 가능한 IP는 단일 IP 및 IP 대역, 모두 허용으로 등록할 수 있습니다.
    (예) 192.168.0.110, 192.168.10.*, 192.*, *
  • 토큰은 영문 또는 숫자, 특수문자를 포함하여 16자리 이상으로 등록하여 주십시오.
1) Authentication Information fieldset
| Input | Path | Width | Description |
|---|---|---|---|
| Login ID | login_id | 200px | User ID to be issued the token (Account registered in User screen) |
| Allowable IP | ip | 400px | Single IP or wildcard pattern (Refer to IP Patterns below) |
| Auth Token | token | 700px | Enter manually or use the Auto Generate API Token button on the right |
| Auto Generate API Token | (Button) | Auto | generate() — Automatically generates a secure token of 16+ characters |
2) Additional Attributes fieldset
| Input | Path | Width | Description |
|---|---|---|---|
| Description | description | 700px × 100px (Text area) | Note on which system/integration it will be used for |
Form Submission
| Button | Position | Action |
|---|---|---|
| List(☰) | Left | Return to token list screen |
| Save | Right (Blue, 100px) | Save after input validation |
API Token Deployment
Simply Saving a token does not apply it to the authentication server. To actually use registered, modified, or deleted tokens, you must click the API Token Deployment button.
| Item | Description |
|---|---|
| Button Location | Right side of the token list panel header |
| Button Label | "API Token Deployment" |
| Tooltip | "Deploys registered, modified, and deleted tokens to the authentication server so they can be used." |
| Action | deployToken() — Batch deploys changed tokens to the authentication server |
Operational Safety Procedure: When registering a new token, remember to perform API Token Deployment so it can be used externally immediately. Conversely, if you delete a token in use, external calls will be blocked immediately after deployment.
Allowable IP Patterns
| Pattern | Meaning |
|---|---|
192.168.0.110 | Allow only a specific single IP |
192.168.10.* | Allow range 192.168.10.0 ~ 192.168.10.255 |
192.168.* | Allow range 192.168.0.0 ~ 192.168.255.255 |
192.* | Allow range 192.0.0.0 ~ 192.255.255.255 |
* | Allow all IPs (Not recommended for security) |
In operational environments, please restrict to a single IP or C-class (
x.x.x.*) range whenever possible.
Use Case Scenarios
| Scenario | Procedure |
|---|---|
| Issue New Operator Account | User → Add User → Enter Login ID, Password, Name, Email, Role (USER) → Save |
| Grant API Permissions to External Analyst | 1) Security Policy → Register API analysis policy 2) User → Add new user, assign Role API + Security Policy 3) API Authentication Token → Issue token for that user, restrict IP |
| Issue API Token for MES Integration | API Authentication Token → Add → Login ID (Integration-dedicated account) + IP Pattern + Auto Generate → Save → API Token Deployment |
| Rotate Active Token | Issue new token → Apply new token to external system → Delete old token → Deploy |
| Deactivate Terminated Employee Account | User List → User Action → Delete (or demote role to USER and change password) |
FAQ
Q. The password input field is missing in the user edit screen.
A. This is normal behavior. The password field is only displayed during new registration (mode='I'). To change a password, the user must log in and navigate to the User menu → "Change Password". If an administrator must force a reset, delete and re-register the user or use a separate password reset procedure.
Q. The security policy ID is automatically assigned. Can I set it manually?
A. The Security ID is automatically assigned by the system (read-only). For a human-identifiable name, use the Security Name field with only English, numbers, and _.
Q. The detailed permissions in the security policy are empty. A. The asset-unit permission granting UI was deactivated as of 2026-03-21. Currently, permissions are determined by the user role (ADMIN/API/USER). Security policies are used for group classification via name and description.
Q. I registered an API token, but external calls are not working. A. After registering, modifying, or deleting a token, you must click the API Token Deployment button. Also, verify that the calling side's IP is included in the token's "Allowable IP" pattern.
Q. I changed the "Allowable IP" of a token. Is it applied immediately? A. You must click API Token Deployment after the change for it to be reflected on the authentication server. Until deployment is complete, external calls will operate under the previous IP policy.
Q. What format of token is created during auto-generation? A. A secure token of 16+ characters consisting of English, numbers, and special characters is randomly generated. For security reasons, please use auto-generation rather than entering simple tokens manually.
Q. Why is a security policy mandatory for API users (Role API)? A. This is to specify which permission group the API call belongs to. It is managed at the group level in preparation for future permission policy enhancements.
Q. Can I force a password policy (length, complexity)? A. This depends on the operating environment settings and is not an item you can change directly on this screen. If a policy change is required, contact the administrator via system settings.
Q. Can I prevent simultaneous user logins? A. By default, simultaneous logins are permitted. You can change the operating environment settings to allow only a single session; please contact the administrator.
Q. Where can I see the token usage history? A. Token usage history can be found in the SERVER application logs on the Diagnostic screen. Authentication failures are recorded at the ERROR level.
Related Screens
- Login — User login procedure and menu differences by role
- Diagnostic — Authentication failure and token usage history logs
- System > Settings — Operating environment settings such as password policies